

ECLOUD / 06
Connect the eCloud VPN on Linux and Windows
Access your company’s private services with WireGuard and check the connection.
- Get your profile
- Connect WireGuard
- Open your service
Arrows point to real controls. Enlarge any detail. Names and options may vary by version and account permissions.
What the VPN does and what you need
A VPN creates a connection tunnel between your device and the authorised private network. It lets you reach services that are not directly published on the Internet. Each application still requires its own account.
- Internet access and permission from your organisation.
- WireGuard installed, with administrator assistance if required.
- A personal
.confprofile generated for this device. - The exact private address of the service you need.
Desktop references: Ubuntu/Debian and Windows 10/11. Always use the official WireGuard installer.
01 · Obtain the connection file
- In eCloud, open VPS → Mi red (My network).
- Under Accesos VPN, an authorised administrator names the device and creates access. End users should receive their profile through a secure channel.
- Download the
.conffile in the confirmation screen. The screen warns that this configuration is shown only once. - Store it securely. Do not send it to groups or reuse the same profile on several devices.
- Name
- portatil-demo
- Action
- Crear acceso
- Result
- Download your .conf file through a secure channel.
One device, one profile. Do not share QR codes or keys.
Crear acceso
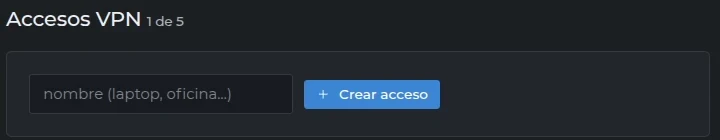
01Use an identifiable name, such as accounting-laptop. The next screen contains a secret file and QR code: store them securely.
Configuración de acceso
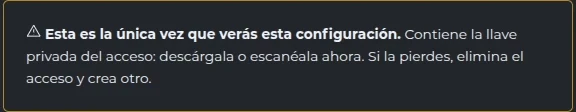
01The configuration is shown once and contains the private key. Download before closing; if lost, request access revocation and replacement.
02A · Linux: install and prepare the profile
On Ubuntu/Debian, open your computer’s Terminal. Run these commands locally with permission to use sudo. Do not run them on the remote server.
- Install the tools with the command below. Password entry may show no characters; this is normal.
- Find the downloaded file in your file manager and check its exact path.
- Replace the example path in the second command with your file’s path; keep quotes around paths containing spaces. The destination uses the name ecloud.
- Restrict access to the file. If
/etc/wireguard/ecloud.confalready exists, do not overwrite it; ask your administrator.
sudo apt install wireguard
sudo install -m 600 "/ruta/al/perfil-descargado.conf" /etc/wireguard/ecloud.conf- apt install
- Installs WireGuard on your computer.
- install -m 600
- Copies the profile and restricts read/write to its owner.
- File path
- Replace /ruta/al/perfil-descargado.conf with the actual path; do not copy the placeholder.
Linux
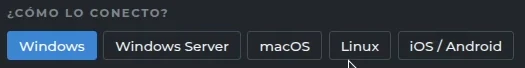
01Select your system tab. Do not paste Linux commands into PowerShell: Windows uses its own client and instructions.
03A · Linux: connect and disconnect
Start the tunnel and check its status:
sudo wg-quick up ecloud
sudo wg show ecloud
Verify: open your application’s authorised private address. After generating traffic, look for a recent latest handshake and transferred data. A created interface alone does not prove connectivity.
To disconnect:
sudo wg-quick down ecloudOptional: connect when Linux starts
Only if your organisation approves and the manual connection already works:
sudo systemctl enable wg-quick@ecloudTo disable automatic startup, use sudo systemctl disable wg-quick@ecloud. This does not disconnect an already active tunnel.
- 01wg-quick up: connect
- 02Open the private service
- 03wg show: check handshake
- 04wg-quick down: disconnect
Conectado
01This is an initial check. Also open the authorised private resource and verify the application responds.
02B · Windows: import and activate
- Open the official WireGuard download page and choose Windows Installer.
- Install with administrator authorisation and open WireGuard.
- Select Import tunnel(s) from file. If profiles already exist, look under Add Tunnel.
- Choose the eCloud
.conffile and verify the correct profile appears. - Select it and press Activate.
- Open your private service and verify it works. When finished, select Deactivate if company policy allows.
VPN does not remove authentication in Odoo or other systems. If Windows requires permissions you lack, ask for help; do not disable antivirus or firewall to continue.
- 1 · Import
- Import tunnel(s) from file → select your .conf.
- 2 · Select
- Check the tunnel name before activating.
- 3 · Activate
- Activate → wait for active status.
- 4 · Verify
- Open the private application. If it fails, check profile, URL and permissions.
- 5 · Disconnect
- Deactivate when finished, according to company policy.
If it does not connect
- “No such file or directory”
- Check the actual download path and filename; do not alter keys or addresses to fix it.
- Active tunnel, application unreachable
- Check Internet, correct profile, private address and service status. Ask for route and permission checks if needed.
- Lost or exposed profile
- Request revocation and replacement. Do not borrow a colleague’s profile.
For support, provide OS, time, status and error without the configuration file, QR or keys.
Traffic through the VPN depends on profile routes. If you only need private services, confirm the configured scope with your administrator; do not change AllowedIPs yourself.
Help and references
Available options depend on the service, version and your account permissions.
Request support ↗