Connected sources
Events of servers, identities, networks and applications according to scope.
TRUSTNET SECURITY / SOC · Security Operations
Centralize signals of your infrastructure to detect relevant activity, analyze your context and coordinate scaling.
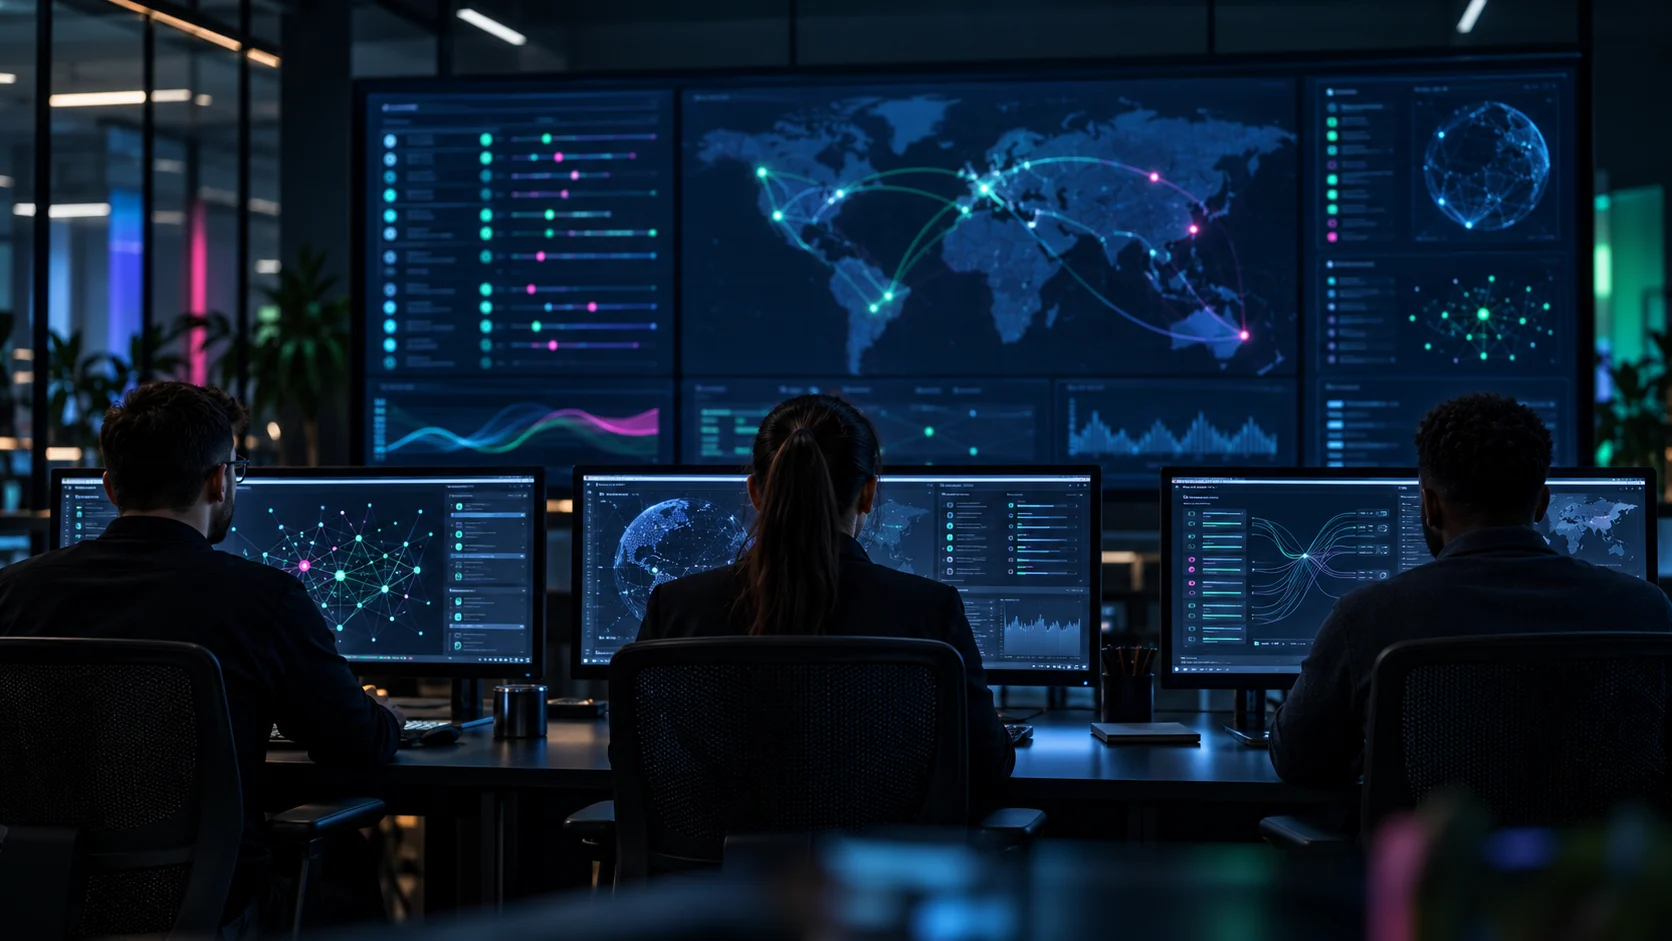
Events of servers, identities, networks and applications according to scope.
Correlation, validation and classification of alerts.
Communication with responsible and registration of actions.
OBSERVAR · CORRELATION · ACTUAR
We design detection cases for your risks and adjust the signals to reduce noise. The integrations, retention and operational coverage are agreed before starting.
Relating identity, origin, schedule and context before climbing.
Review authorization, scope and related signals.
Correlate searches and rules of protection with the responsible team.
RESULTS THAT YOU CAN USE
HOW WE WORK
Define sources, permits and quality of records.
Apply cases of use and correlate events.
Validate context and priority.
Coordinate actions with those responsible defined.
We're backing up your DUDs.
Investment as far as possible. We count on your assets, objectives and needs.
No. Coordinates with infrastructure and business managers to analyze and manage security events.
No. Alerts must be validated and related to their context before categorizing them as incidents.
They are defined in the proposal according to the sources, volumes and needs of the service.